Why You Need an Audit Trail, Not Just a Finished Report
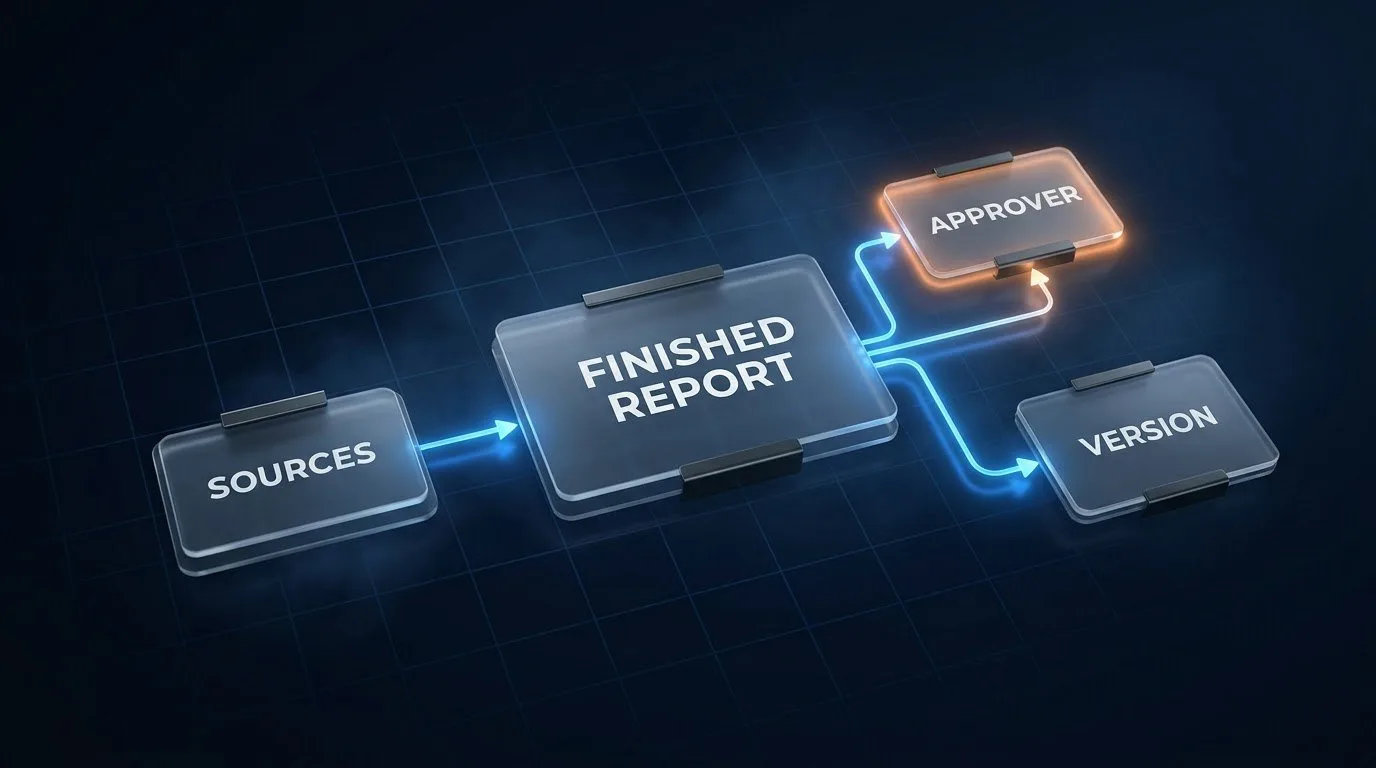
An audit trail records four checkable facts for each piece of work: what was used, who approved it, when, and on which version. A finished report tells you none of that. The need appears months later, when someone asks why the report says what it says.
Ask most teams to explain, six months after the fact, exactly what went into a specific report and who signed it off, and the honest answer is usually “let me check”, followed by a search through email and shared drives. The deliverable exists. The story of how it got there does not. This article explains what an audit trail records, why it is a design feature rather than an afterthought, and how to test whether one actually works.
01. Why it becomes a problem later, not now
At the moment work is issued, everyone involved remembers how it happened: who reviewed it, what source data it drew on, why a particular judgement call was made. That context fades within weeks, faster than anyone expects, because nobody wrote it down at the time. It lived in people’s memory.
The gap only becomes visible when someone needs the answer: a client query, a compliance review, a dispute about what was agreed.
02. What an audit trail records
A finished deliverable tells you nothing about how it was produced. An audit trail records four checkable facts: what was used, who approved it, when, and on which version. Not a general sense that the process was followed.
| Fact | What it looks like in a trail | What it looks like without one |
|---|---|---|
| What was used | Source material and evidence, attributed to the item each supports | Documents loose in a folder |
| Who approved it | A named, accountable role | An email that might have been a yes |
| When | A timestamp tied to a specific action | An estimate |
| On which version | The exact version that went out | “The report”, as if it were one static thing |
Work gets revised, so “the report” is a sequence of versions. The trail has to say which one actually went out. For why approval should be tied to a role rather than a person, see access that follows the role, not the person.
03. Why it matters more once AI is involved
When a workflow includes AI-assisted drafting that a person reviews and approves before anything ships, the audit trail is what shows that sequence happened for a specific piece of work. It is the difference between a policy and evidence that the policy was followed, for this deliverable, on this date. The commitments themselves are set out in why AI sits in the middle, not at the end and in what we do with your data.
04. A test you can run six months later
Pick one finished piece of work and ask three questions:
- What source supported this figure? The answer should point to a specific item, not a folder.
- Who approved this version, and when? The answer should name a role and a time.
- What changed between the draft and the issued version? The answer should be a record, not a recollection.
If answering any of them means searching email or asking whoever happened to work on it, there is no trail.
05. Where this lives in what we build
Traceability is one of the controls built into every connected delivery system, alongside access, testing and reporting. It is part of the design, not added afterwards because a reviewer asked for it. The trail runs from source material through approval to issued output, and it lets a quality or compliance reviewer answer a specific question about a specific piece of work without asking the person who happened to work on it and hoping they remember.
06. What it actually gets used for
Rarely for the reason people build it. Most audit trails exist because a compliance reviewer required one, and are then used, months later, for something different: settling a disagreement about what was agreed, confirming a figure that is now being questioned, or answering “why does this say what it says” when the person who wrote it has moved to another project.
The test of an audit trail is not whether it exists but whether it answers the question when someone finally needs it to.
07. Four questions to ask any supplier
- Can you show me what went into a specific past deliverable? A generic description of a process is not an answer.
- Is approval recorded against a version? If not, you cannot tell which version was approved.
- Is the trail created as the work happens, or reconstructed afterwards? Reconstruction is memory with a timestamp.
- Who can see the trail, and for how long is it kept? A trail nobody can reach is not one.
08. Frequently asked questions
What is an audit trail?
A record of specific, checkable facts about a piece of work: what was used, who approved it, when, and on which version.
Why do I need one if I have the finished report?
Because a finished report does not show how it was produced. The trail answers questions months later, when the people involved may have moved on.
Does an audit trail matter more with AI?
Yes. It shows that review and approval happened for this deliverable, on this date, not just that the workflow is designed to work that way.
Is the audit trail added afterwards?
No. Traceability is one of the controls built into the system, not an afterthought.
How can I test whether a trail works?
Pick a finished piece of work six months old and ask what supported a figure, who approved the version and when, and what changed between draft and issued.
09. Next step
See the governance commitments this sits alongside: access, review, testing and exit. How the work is controlled →